Google Cloud infrastructure
CLOUD RUN + CLOUD STORAGE
Your Neural Fabric runs on Google Cloud infrastructure, with business data stored in the United States.
Security
Explore how Qorbit protects access, encrypts data, and records the history of your Neural Fabric.
CLOUD RUN + CLOUD STORAGE
Your Neural Fabric runs on Google Cloud infrastructure, with business data stored in the United States.
TLS + ENCRYPTION AT REST
Data is encrypted in transit and at rest. Stored AI provider credentials use AES-256-GCM encryption.
SAML + OIDC
Enterprise customers can connect their organization’s identity provider, including Entra ID, Okta, or Google Workspace. Requires organization setup.
TENANT-SCOPED ACCESS
Authenticated requests are tied to a workspace. Business data is stored and retrieved within that tenant’s scope.
ENCRYPTED STORAGE
Stored connector tokens and AI provider keys are encrypted. Disconnecting a connector removes its stored credentials.
YOUR KNOWLEDGE REMAINS YOURS
Qorbit does not use your Neural Fabric data to train AI models. AI features may send relevant content to configured providers to process your requests.
SHA-256 HASH-LINKED PROVENANCE
Inspect the recorded actor label, time and operation for an entity change. Where available, compare the property values before and after an edit. Hash-linked records support verification of the recorded history.
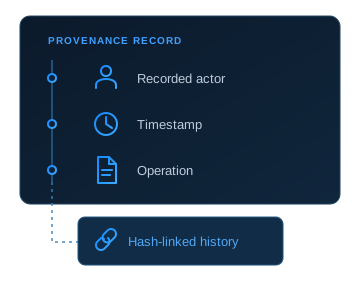
Coverage applies to governed writes. Provenance is not immutable storage.
Request access, export, correction, or deletion of your data.